Pakistan Issues Cyberattack Alert: Could Compromised Keys Put Websites at Risk?
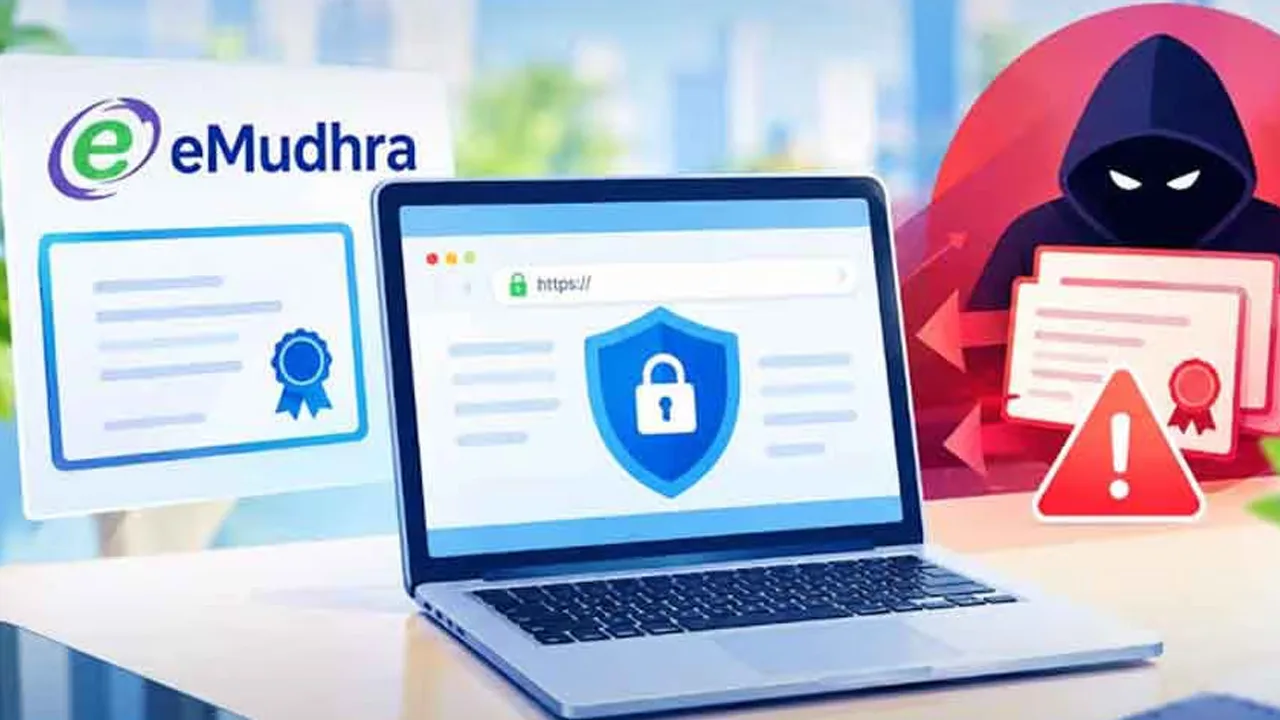
Pakistan's National CERT warns of cyber risks after eight eMudhra security keys are compromised, urging organisations to update systems and block affected certificates.
Pakistan's National Cyber Emergency Response Team (National CERT) has issued a cybersecurity warning after eight digital security keys linked to eMudhra were found to have serious security weaknesses. The issue could expose some digital systems to risks such as fake websites, online impersonation, and the interception of internet traffic.
Government departments, financial institutions, businesses, and operators of critical information systems have been advised to take protective measures to reduce potential risks.
How Were the Security Keys Compromised?
The security issue involved eight intermediate digital certificates used to help establish trust between websites, software, and users. The private keys associated with these certificates were generated with insufficient randomness, making them possible to recover.
Six of the affected certificates were related to website security, while two were used for software code signing. If misused, these keys could allow attackers to create fake certificates that appear trustworthy.
What Risks Could Users Face?
Compromised security certificates can create opportunities for cybercriminals to impersonate legitimate websites or services. In certain circumstances, this could allow attackers to intercept or modify communications between users and online platforms.
The risk depends on whether a system still trusts the affected certificates and whether the necessary security protections have been applied.
However, the existence of a security weakness does not mean that every website or user has been affected. The incident has prompted security teams to take steps to block the compromised certificates.
What Steps Should Organisations Take?
Organisations have been advised to review their systems and follow relevant security guidance. Key precautions include:
Updating browsers, operating systems, and security software.
Blocking or removing trust in affected certificates.
Checking systems for certificates linked to the compromised keys.
Monitoring for unusual activity and suspicious digital certificates.
Following official cybersecurity advisories and applying recommended fixes.
Users should also keep their devices updated and avoid ignoring browser security warnings.
What Happens Next?
The incident highlights the importance of regular security checks and strong digital certificate management. Organisations that rely on secure online connections need to ensure their systems no longer trust affected certificates.
Although protective measures have been introduced by major technology providers, organisations should verify that their own systems and applications have received the necessary updates.
Related stories
 Cyber Security
AI-Discovered Software Flaws May Cause More Outages
 Cyber Security
Naqvi Urges Online Caution; 600 Arrested in Cyber Cases
 Cyber Security
PHP Flaws Found by AI: What Websites Need to Know
 Cyber Security
FBI Arrests OpenAI Engineer Over Hidden Recording Device
· 2 min read Cyber Security
NCCIA Arrests Three in Faisalabad, Gujranwala and Kasur After AI-Assisted Alert on Suspected Child Exploitation Material
 Cyber Security